One consistent framework across every non-human identity
Knowledge On TAP helps establish a vendor-neutral Non-Human Identity Security framework to discover and classify identities, assign ownership, control authentication and authorisation, apply least privilege, monitor activity and manage the full lifecycle — extending consistent Identity Security principles across both Human and Non-Human identities.
Gain Visibility. Control Privilege. Reduce Non-Human Identity Risk.
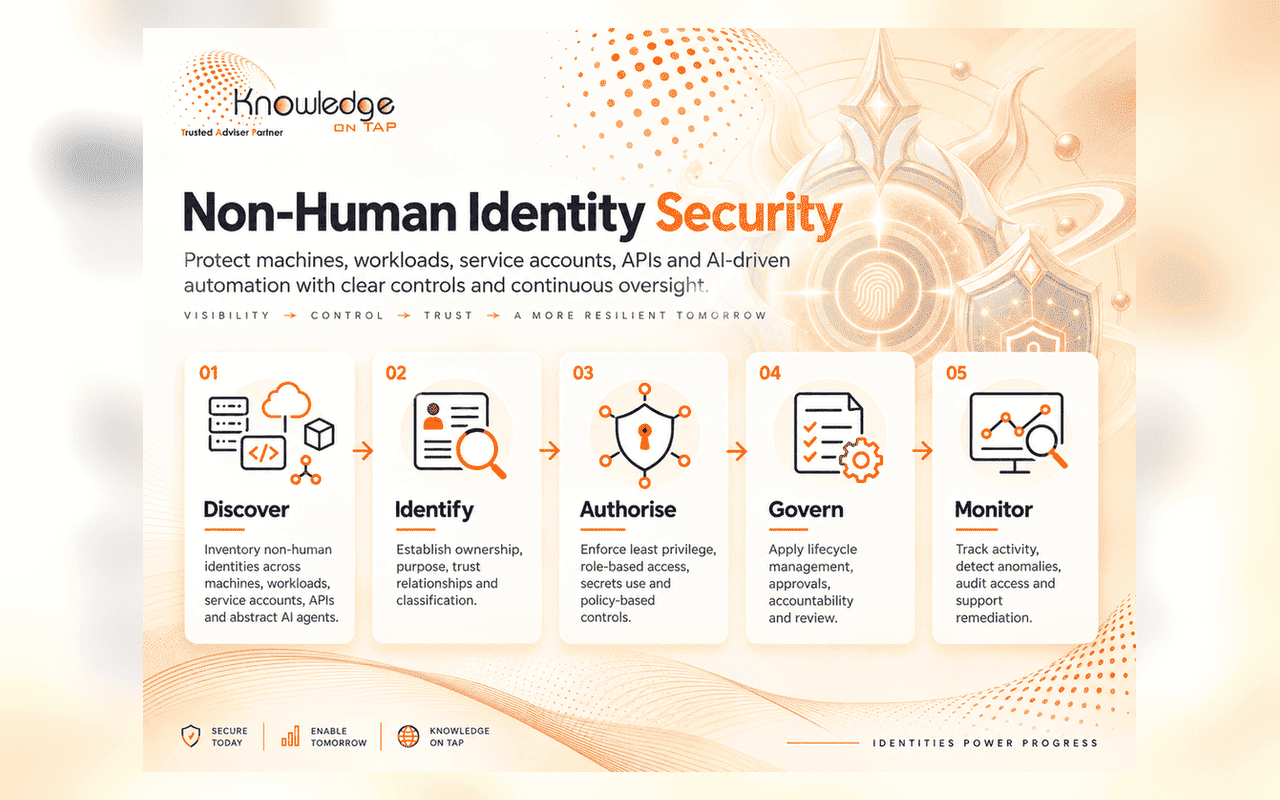
Gain Visibility. Protect Credentials. Control Machine Access.
Machines, applications, services and automated processes increasingly rely on credentials and permissions to access critical systems — often at scale and without the same visibility, ownership or governance applied to human identities. We help you discover machine identities, assign clear ownership, protect credentials and secrets, apply least privilege, govern access and continuously validate whether permissions remain appropriate.
Replace Static Credentials. Strengthen Trust. Control Workload Access.
Cloud-native applications, containers, microservices, APIs, DevOps services and serverless functions increasingly need to authenticate directly to other workloads and resources — creating risk when access depends on unmanaged, shared or long-lived credentials. We help establish Workload Identity Security using trusted workload identities, strong authentication, least-privilege authorisation and lifecycle controls across cloud, hybrid and modern application environments.